eMudhra shares fall 37% in two sessions after key compromise
eMudhra shares hit an intraday low of Rs 345 after a security incident involving eight intermediate CA certificates. MeitY said Indian digital signature and eSign services were unaffected, while the company warned of unquantifiable reputational risks.
BharatVox Telugu Desk · 2 hr ago · మూలం: Economic Times Markets
ఈ కథనం భారత్వాక్స్ ఆంగ్ల మూలం నుండి తెలుగులోకి అనువదించబడింది. ఆంగ్ల మూలం చదవండి →
తెలుగు అనువాదం సిద్ధమవుతోంది… (మొదటిసారి కొద్దిగా సమయం పట్టవచ్చు)
eMudhra shares fell another 20% to an intraday low of Rs 345 on Thursday, October 22, taking their two-session decline to around 37% after a security incident involving compromised private keys linked to eight intermediate Certificate Authority (CA) certificates. Economic Times Markets reported the price fall and the responses from the company and the Ministry of Electronics and Information Technology (MeitY).
MeitY said eMudhra’s Indian Digital Signature Certificate (DSC) and eSign services remain unaffected. The ministry described the impact on Indian websites and applications as very limited and brief, and said it was working with stakeholders to address the incident.
The latest sell-off followed a 20% decline on Wednesday after the Indian Computer Emergency Response Team (CERT-In), the Centre’s nodal cybersecurity agency, issued an urgent advisory. The Rs 345 price is a reported intraday low, not a closing price.
Indian services separate from affected global business
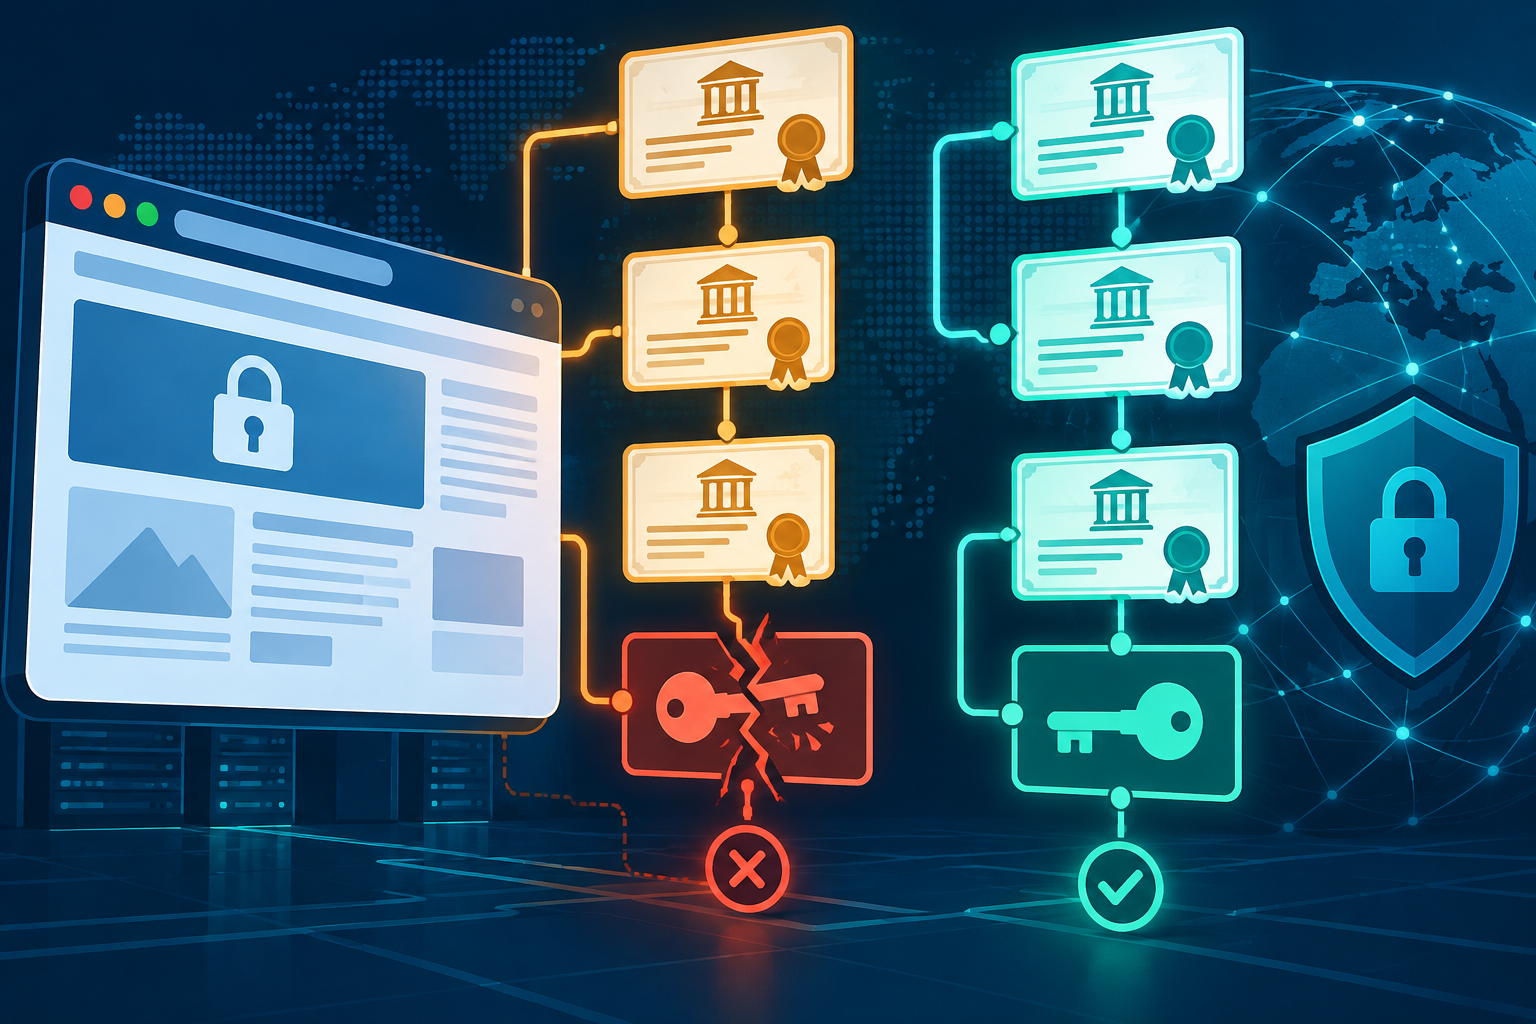
The ministry distinguished between two parts of eMudhra’s operations. Its Indian digital signature and eSign services fall under the Controller of Certifying Authorities (CCA), which operates under MeitY. The other business supplies certificates trusted by major browsers and operating systems to secure websites, software and online communications.
According to MeitY, the incident is confined to the international business, which operates under a global trust framework and undergoes independent audits, including WebTrust audits by BDO International. The ministry said it does not audit that part of the company’s operations.
The eight affected certificates were issued under eMudhra’s global Public Key Infrastructure (PKI), the system used to establish trust in digital certificates and secure online connections. The company said its Indian DSC and eSign services use infrastructure separate from the global Transport Layer Security (TLS) business and continue to operate normally.
Company points to flaw during key generation
In a regulatory filing, eMudhra attributed the problem to a flaw in its key-generation ceremony. It said a wrap/unwrap step produced a second, weak set of keys alongside the original strong keys, and that the weak keys were subsequently published to browser root stores. Its investigation into the root cause remains under way.
The company said the relevant roots and issuing CAs had undergone independent audits for two consecutive years and had been included in browser trust lists since mid-2025.
According to eMudhra’s account, an independent researcher discovered the previous weekend that the weak keys could be reverse-engineered and notified the root programmes run by Apple, Google, Microsoft and Mozilla. The company raised the possibility of AI-assisted techniques; that possibility is not an established finding.
Small revenue exposure, uncertain reputational cost
eMudhra said the affected global TLS business accounts for around 1% of its revenue, indicating limited direct revenue exposure. It nevertheless cautioned that the incident could damage its reputation and that the extent of that risk could not be quantified.
The company said it was working directly with potentially affected customers to provide replacement certificates and avoid disruption to critical services. It was also coordinating with the browser root programmes while continuing its root-cause investigation.
ఈ కథనం భారత్వాక్స్ ఆంగ్ల మూలం నుండి తెలుగులోకి అనువదించబడింది. ఆంగ్ల మూలం చదవండి →